Drive specialist NORD DRIVESYSTEMS implemented the processes and structures required for the Cyber Resilience Act in due time.
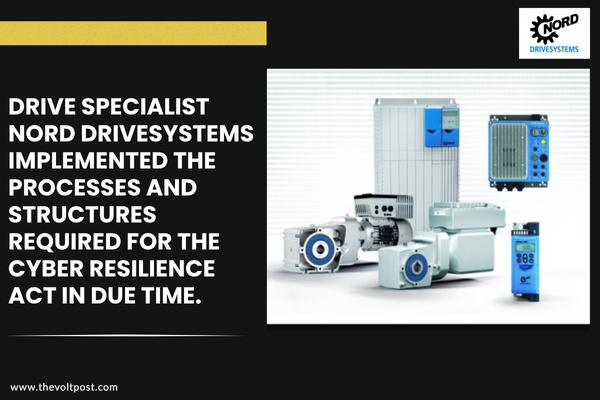
The company thus fulfils the statutory reporting obligations for actively exploited vulnerabilities from 11 September onwards. Full CRA compliance of the affected products is scheduled to be available by 11 December 2027.
As of 11 September 2026, the reporting obligations for actively exploited vulnerabilities will apply according to the Cyber Resilience Act (CRA) of the European Union, Regulation (EU) 2024/2847. NORD DRIVESYSTEMS set up the required processes and structures and fully complies with the new requirements.
Binding framework for networked products
The Cyber Resilience Act became applicable on 10 December 2024. It stipulates binding cybersecurity requirements for products containing digital elements, which are offered in the European single market.
NORD welcomes this regulation. “Uniform safety standards increase confidence in networked industrial products, and provide planning security for manufacturers and customers”, says Jörg Niermann, Head of Marketing at NORD.
As of 11 September 2026, manufacturers will be obliged to report any actively exploited vulnerability. The full requirements of the CRA will apply as of 11 December 2027 for newly introduced products. NORD strives to meet this deadline.
Four frequency inverters affected
Within the drive manufacturer’s product range, the networked frequency inverters NORDAC ON, NORDAC LINK (as a motor starter and frequency converter), NORDAC FLEX and NORDAC PRO fall within the scope of the CRA.
The product requirements have been evaluated under their operating conditions in accordance with the CRA.
A threat and risk analysis was conducted for this purpose. Furthermore, the requirements of IEC 62443-4-2 were evaluated in this context according to Security Level 1.
Implementation along an internal roadmap
NORD follows an internal roadmap to integrate the required safety standards into the product portfolio.
According to the “Secure by Design” principle, cybersecurity is already considered during product development. The development processes are adjusted to the IEC 62443-4-1 standard.
By 11 December 2027, complete declarations of conformity, technical documentation and software bills of material will be available for all relevant products.
Documentation for machine manufacturers and OEM customers
 NORD provides machine manufacturers and OEM customers with declarations of conformity, technical documentation on the implemented safety functions, and self-declarations on the implementation status of IEC62443.
The documentation will support customers in providing evidence of the requirements within their own conformity chain.
Vulnerabilities can be reported via reporting platform, CLICK HERE
Here, NORD also provides further information on the implementation of the CRA, and lists contact persons for product-specific questions.